
How to Fix a VPN IP Leak in 2026
A VPN that leaks your real IP, DNS requests, or WebRTC address quietly defeats the entire point of using one. Here’s exactly how to test for every kind of leak, fix each one in minutes, and choose a VPN that doesn’t leak in the first place.
What Is a VPN IP Leak (and Why It Actually Matters)
When you connect to a VPN, the app is supposed to build a single encrypted tunnel between your device and a remote server, then push every byte of your internet traffic through it. Websites, apps, and your internet provider should only ever see the VPN server’s address, not yours. A leak is any situation where some piece of traffic escapes that tunnel and travels over the open internet with your real details attached.
That “some piece of traffic” is the dangerous part. A leak doesn’t have to expose everything to be a problem. If even your DNS lookups slip out, your internet provider can rebuild a near-complete list of the sites you visit. If your WebRTC-enabled browser hands over your home IP address to a web page, an advertiser or a streaming service can tie your session straight back to you. The VPN icon still says “Connected,” the app still looks green, and you feel protected, while your real location quietly bleeds out in the background.
This is what makes leaks uniquely nasty compared with simply forgetting to switch a VPN on. When the VPN is off, you know you’re exposed. When it’s leaking, you have a false sense of security, which is arguably worse: you’ll do things assuming you’re private that you would never do otherwise. People who rely on a VPN to bypass censorship, to torrent safely, to research sensitive topics, or to avoid targeted price discrimination all depend on the tunnel being watertight. A single leak can undo months of careful habits.
It’s worth being clear about who this affects, because leaks aren’t only a concern for people doing something unusual. Anyone using a VPN to keep their internet provider from selling their browsing habits, to stop a streaming service from tying a session to their home, to shop without region-based price discrimination, or simply to keep public Wi-Fi private is relying on the tunnel holding. On a shared or public network, a leak is even more serious: the network operator sits in the same position as an internet provider and can see anything that escapes the tunnel. In other words, the more you value the privacy a VPN promises, the more a silent leak costs you.
The good news is that leaks are almost always fixable, and usually with settings you already have. The overwhelming majority come down to four causes, they can be diagnosed in about two minutes with free tools, and the fixes are the same regardless of which VPN you use. The rest of this guide walks through each one in plain language, then shows you the setup and the providers that prevent leaks from happening at all.
The 4 Types of VPN Leak You Need to Know
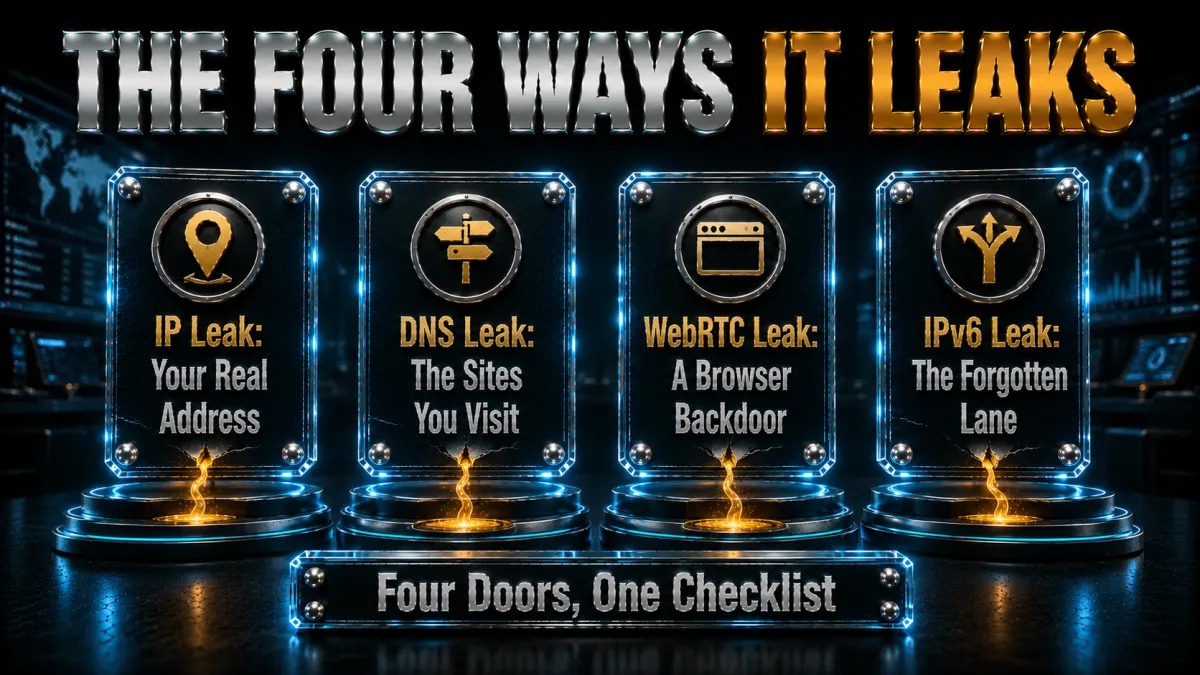
“IP leak” is often used as a catch-all, but there are really four distinct ways your identity escapes a VPN tunnel. Each has a different cause and a different fix, so it helps to understand them separately before you start testing. Here’s the honest overview.
| Leak type | What escapes | Usual cause | Main fix |
|---|---|---|---|
| IP address leak | Your real IPv4 address | Dropped connection, no kill switch | Enable kill switch |
| DNS leak | The sites you look up | Queries go to ISP resolver | VPN DNS-leak protection |
| WebRTC leak | Real IP via the browser | Browser peer-to-peer feature | Disable/limit WebRTC |
| IPv6 leak | Your real IPv6 address | VPN only tunnels IPv4 | Disable or route IPv6 |
An IP address leak is the classic case: your device briefly connects to the internet directly instead of through the VPN, exposing your real IPv4 address. This most often happens when the VPN connection drops for a second, while switching Wi-Fi networks, waking from sleep, or when a server hiccups, and there’s no kill switch to freeze your traffic in that gap.
A DNS leak is subtler. DNS is the internet’s address book: every time you type a domain, your device asks a DNS resolver to translate it into an IP address. Those queries are supposed to travel inside the tunnel and be answered by the VPN’s own private resolver. In a DNS leak, they instead go to your internet provider’s resolver, handing your provider a running log of every site you visit, even though the rest of your traffic is encrypted.
A WebRTC leak comes from your browser, not your VPN. WebRTC is a built-in feature that powers video calls, screen sharing, and peer-to-peer connections directly in the browser. To make those connections work, WebRTC can ask your device for its real IP address and share it with a web page through a mechanism that sidesteps the VPN tunnel entirely. It’s one of the few leaks a VPN can’t always catch, because it happens inside the browser’s own code.
An IPv6 leak is increasingly common as more networks adopt the newer IPv6 addressing standard. Many VPNs were built to tunnel IPv4 traffic and either ignore IPv6 or handle it poorly. If your device and network both support IPv6 but your VPN doesn’t route it, your IPv6 traffic goes straight out over the open internet, carrying your real address with it while your IPv4 stays safely tunnelled.
How to Test Your VPN for Leaks (Step by Step)
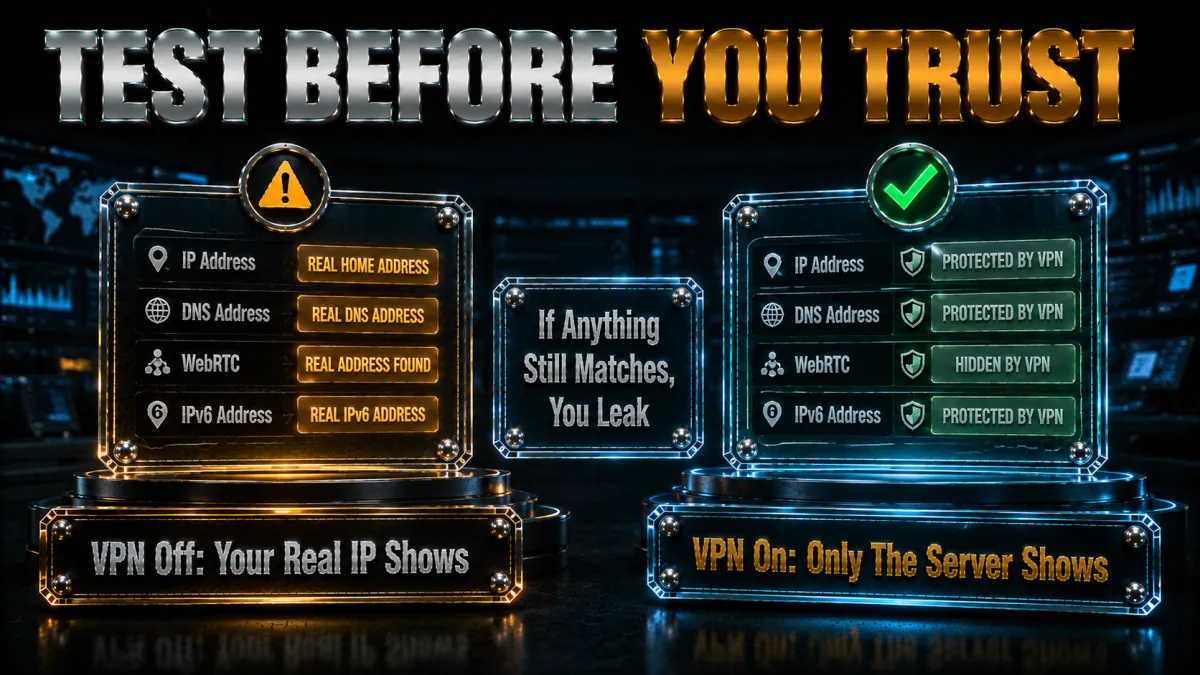
Before you fix anything, confirm whether you actually have a leak and which type it is. The whole test takes about two minutes and costs nothing. The principle is simple: connect your VPN, then check what the internet sees. If any test shows your real IP address, your real location, or your own internet provider, you have a leak.
- Note your real details first. With the VPN off, visit whatismyipaddress.com and write down your real IP address and the city and provider it reports. This is your baseline, the information that must never appear once the VPN is on.
- Connect your VPN to any server, ideally in a different country from where you actually are. Give it a few seconds to fully establish the tunnel.
- Run a combined leak test. Go to ipleak.net or browserleaks.com/ip. These pages check your IPv4, IPv6, DNS, and WebRTC results all on one screen, the fastest way to see everything at once.
- Check the IP address. The IPv4 shown should match the VPN server’s country, not your real one. If you see your real IP or home city anywhere, you have an IP leak.
- Check the DNS servers. Scroll to the DNS section. Every resolver listed should belong to the VPN or its country, never your own internet provider. Your ISP‘s name appearing here is a DNS leak. For a dedicated check, dnsleaktest.com’s “Extended test” is the gold standard.
- Check WebRTC. Look at the WebRTC section on ipleak.net or run browserleaks.com/webrtc. If your real public IP appears there, WebRTC is leaking through your browser.
- Test the kill switch. With the VPN connected and a leak page open, briefly disconnect your internet or force the VPN to drop (toggle the server). Your internet should freeze completely until the tunnel is restored. If pages keep loading with your real IP during that gap, your kill switch is off or not working.
Run these checks whenever you set up a new device, after a major operating-system update, when you switch networks often, or simply once a month as good hygiene. Leaks tend to appear silently after updates reset network settings, so periodic re-testing is the single best habit you can build. If everything shows the VPN server and nothing shows your real details, you’re watertight, and you can skip straight to the leak-proof provider picks below. If something failed, the next sections fix each type in turn.
How to Fix an IP Address Leak
An IP address leak means your real IPv4 address is reaching the internet despite the VPN being on. Almost always, the culprit is a momentary drop in the connection with no safety net to catch it. Work through these fixes in order, the first two solve the vast majority of cases.
1. Turn on the kill switch. This is the single most important setting in any VPN. A kill switch monitors the tunnel constantly and, the instant it detects a drop, blocks all internet traffic until the VPN reconnects. That closes the exact gap where IP leaks happen. Every major VPN has one, in NordVPN, ExpressVPN and Surfshark it lives in the app’s settings, sometimes labelled “Network Lock” (ExpressVPN) or simply “Kill Switch.” Enable it and leave it on permanently.
2. Reconnect, and pick a nearer or less busy server. If a specific server keeps dropping, it may be overloaded or having issues. Disconnect fully, choose a different server, ideally one geographically closer to you for a more stable connection, and reconnect. A fresh, stable tunnel often ends intermittent leaks on its own.
3. Switch your VPN protocol. The protocol is the underlying technology that carries your tunnel. If you’re on an older or unstable protocol, switch to WireGuard (called NordLynx in NordVPN, Lightway in ExpressVPN). WireGuard reconnects faster and holds the tunnel more reliably, which reduces the brief drops that cause leaks. If WireGuard is already selected and you’re still seeing problems, try OpenVPN as a stable fallback.
4. Update the app. Leak-related bugs are patched regularly. Make sure you’re running the latest version of your VPN app from the official site or app store, then re-test. An outdated client is a surprisingly common cause of leaks that “appeared out of nowhere.”
5. Restart your device and router. A stale network stack can force traffic outside the tunnel. A full restart of your device (and your router, if you can) clears cached routes and often resolves a stubborn leak that survives everything else.
A note on phones. Mobile devices leak for a specific, common reason: they constantly switch between Wi-Fi and mobile data. Every handoff is a moment the tunnel can drop, so a system-level “always-on VPN” setting matters even more on a phone than a laptop. On Android, enable “Always-on VPN” and “Block connections without VPN” in the network settings; on iOS, keep the VPN’s own kill switch or “auto-connect” enabled. Together these ensure your phone never quietly falls back to an unprotected connection while you move between networks.
How to Fix a DNS Leak
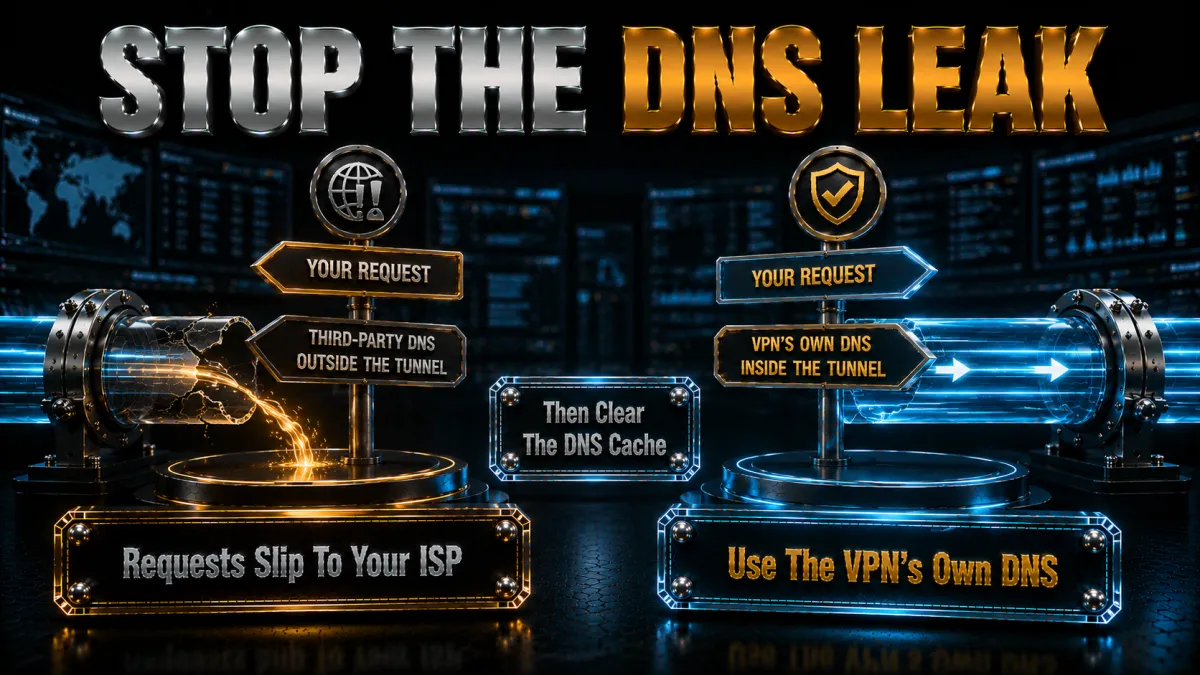
A DNS leak means your device is sending its “what’s the address for this domain?” questions to your internet provider’s resolver instead of the VPN’s. Your provider can’t read your encrypted traffic, but a full log of your DNS lookups is nearly as revealing. Here’s how to seal it.
1. Enable your VPN’s DNS-leak protection. Nearly every reputable VPN runs its own private DNS servers and forces all lookups through them. Look in your app’s settings for “DNS leak protection” or “Use VPN DNS” and switch it on. In NordVPN, ExpressVPN and Surfshark this is enabled by default, if you’ve never touched it, it’s probably already working, and a DNS leak means something is overriding it.
2. Flush your DNS cache. Old cached lookups can keep pointing at the wrong resolver. On Windows, open Command Prompt and run ipconfig /flushdns. On macOS, run sudo dscacheutil -flushcache; sudo killall -HUP mDNSResponder in Terminal. Then reconnect the VPN and re-test.
3. Disable “Smart Multi-Homed Name Resolution” on Windows. This Windows feature sends DNS queries out of every network adapter at once to speed things up, and in doing so, it routes some lookups straight to your ISP, around the VPN. Turning it off is one of the most common DNS-leak fixes on Windows. You can disable it via Group Policy (on Pro editions) or with a small registry change; many VPN apps also handle this automatically once DNS protection is on.
4. Check for a conflicting DNS setting. If you’ve manually set a custom DNS server (say, a public resolver) in your operating system or router, it can override the VPN’s DNS. Set your system DNS back to “automatic” so the VPN can take control, then re-test.
5. Watch out for split tunneling. If you use split tunneling to let certain apps bypass the VPN, those apps may also bypass the VPN’s DNS. Either remove the app from your split-tunnel list or accept that its lookups won’t be private. For maximum privacy, turn split tunneling off entirely.
After any of these, return to dnsleaktest.com and run the Extended test. Every server it lists should belong to your VPN or its host country. The moment your own provider disappears from that list, the leak is closed.
How to Fix a WebRTC Leak (Chrome, Firefox, Edge & Safari)
WebRTC leaks are special because they happen inside your browser, not your VPN. WebRTC is the technology behind in-browser video calls, screen sharing and peer-to-peer file transfer, and to set those up it can quietly ask your device for its real IP and reveal it to a web page. A strong VPN with its kill switch on will often block this at the firewall level, but the most reliable fix is to control WebRTC in the browser itself.
Firefox is the easiest to fully seal, because you can disable WebRTC natively with no add-ons. Type about:config in the address bar, accept the warning, search for media.peerconnection.enabled, and double-click it to set the value to false. WebRTC is now off completely.
Chrome has no built-in switch to fully disable WebRTC, so you have two options. The simplest is a reputable extension such as “WebRTC Leak Prevent” or “WebRTC Control,” which lets you block non-proxied UDP traffic, the exact path a leak uses. Alternatively, open chrome://flags, search for “WebRTC,” and set “Anonymize local IPs exposed by WebRTC” to Enabled; note this only hides your local network address and is a partial fix, so an extension is the safer choice.
Edge, being built on the same Chromium engine as Chrome, uses the same approach: install a WebRTC-blocking extension from the store, or use the equivalent flag. The extension route is the more complete solution.
Safari gives you granular control under Settings → Advanced → “Show features for web developers,” then in the Develop menu you’ll find WebRTC options. Safari is generally more conservative about exposing local IPs than Chrome, but it’s still worth verifying with a test.
One important trade-off: disabling WebRTC entirely will break browser-based video calls, screen sharing, and some collaboration tools like certain web versions of meeting apps. If you rely on those, a good middle ground is to use an extension that blocks leaks only while still allowing connections you initiate, or to keep WebRTC off in your everyday browser and use a separate browser for calls. After making your change, confirm it worked at browserleaks.com/webrtc, your real public IP should no longer appear.
How to Fix an IPv6 Leak
An IPv6 leak happens when your network and device support the newer IPv6 addressing standard but your VPN only tunnels the older IPv4 traffic. Your IPv4 stays safely inside the tunnel while your IPv6 traffic, carrying your real IPv6 address, slips out over the open internet. As IPv6 adoption grows worldwide, this leak is becoming far more common than it used to be.
1. Use a VPN with native IPv6 handling. The cleanest fix is a VPN that either fully tunnels IPv6 or automatically blocks it so it can’t leak. The leading providers now do exactly this, their apps detect IPv6 and either route it through the tunnel or disable it at the connection level, so you never have to think about it. If your current VPN doesn’t, that’s a strong reason to upgrade.
2. Enable IPv6 leak protection in the app. Some VPNs include a specific toggle for this. If yours does, switch it on and re-test. It tells the app to block all IPv6 traffic while connected, closing the leak without any system changes.
3. Disable IPv6 at the operating-system level. If your VPN can’t handle IPv6, the safe workaround is to turn IPv6 off on your device so there’s nothing to leak. On Windows, open your network adapter’s properties and uncheck “Internet Protocol Version 6 (TCP/IPv6).” On macOS, you can set IPv6 to “Off” for your active network in the advanced TCP/IP settings. Almost nothing you do daily depends on IPv6 yet, so disabling it rarely causes problems, and you can re-enable it any time.
4. Disable IPv6 on your router. If you want to cover every device on your network at once, log into your router’s admin page and turn off IPv6 there. This is a heavier hammer, but it guarantees that no device can leak an IPv6 address regardless of its individual VPN settings.
After applying a fix, return to ipleak.net and confirm the IPv6 section either shows the VPN’s address or reports no IPv6 connectivity at all. Either result means the leak is closed.
Clear the DNS cache after fixing a leak
This is the step almost everyone skips, and then wonders why the test results keep flickering between clean and dirty.
Why it matters. While the leak was happening, your device stored DNS answers it obtained outside the tunnel. Until those cached entries expire, some connections keep reusing the old path, so a re-test can look fixed one minute and broken the next.
The flush command, per platform:
- Windows: open Command Prompt and run
ipconfig /flushdns - macOS: open Terminal and run
sudo dscacheutil -flushcachefollowed bysudo killall -HUP mDNSResponder. Both are needed, because the first clears the cache and the second restarts the resolver. - Linux: the command depends on your resolver, most commonly
sudo resolvectl flush-cacheson systemd machines - Android and iOS: toggling airplane mode on and off clears it, and a reboot certainly does
Browsers keep their own separate cache. Chromium browsers hold a DNS cache independent of the operating system. Clear it from the net-internals DNS page, or simply restart the browser. This is worth doing when the leak only appears in browser tests but the system tests come back clean.
Then re-test once more. Flush, reconnect the VPN, and run the DNS test again. Consistent clean results across two or three repeats is the finish line, because from a fresh cache the results you see are the results you will actually live with.
Why the Kill Switch Is Your Single Most Important Setting
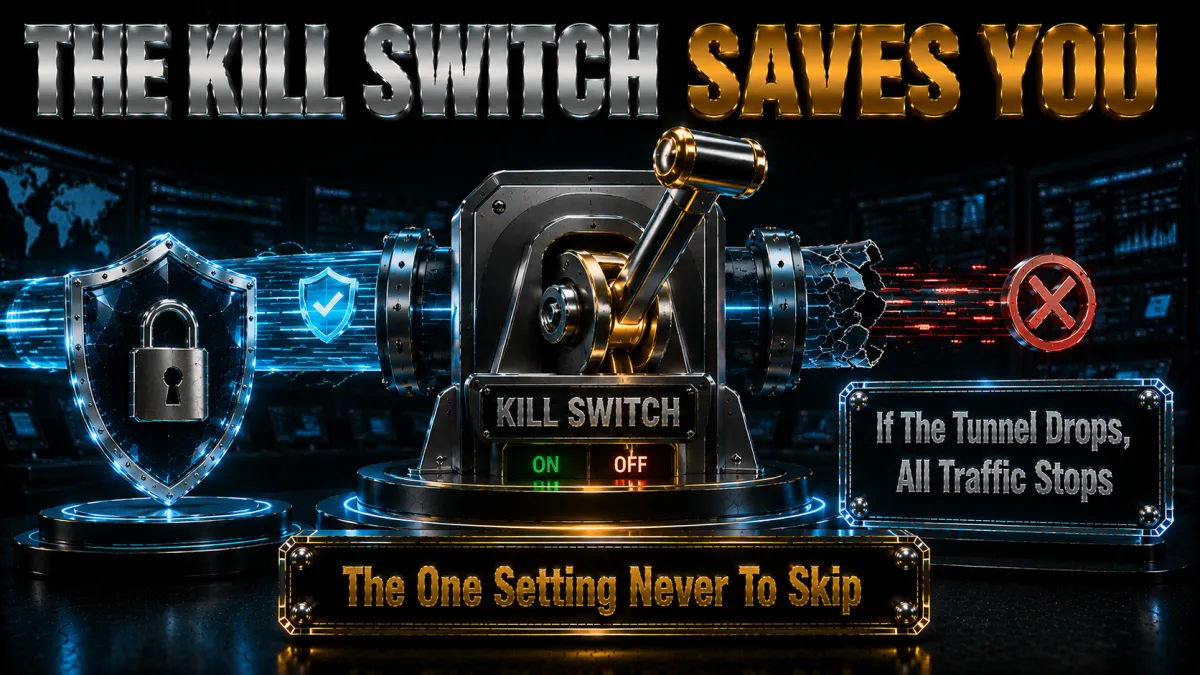
If you take only one thing from this guide, make it this: turn on your kill switch and never turn it off. More leaks are caused by a missing or disabled kill switch than by any other single factor, and it’s the one setting that protects you during the exact moments you can’t see.
Here’s why it matters so much. VPN connections are not perfectly stable, no connection is. They drop for a fraction of a second when you switch from Wi-Fi to mobile data, when your laptop wakes from sleep, when a server rotates, or when your network stutters. In each of those tiny windows, your device instinctively falls back to its normal, unprotected connection and keeps sending traffic. Without a kill switch, that traffic carries your real IP address. You’ll never notice, the drop and recovery happen faster than you can perceive, but a website, tracker, or your internet provider might catch it.
A kill switch removes that risk entirely. It acts as a circuit breaker: the moment the encrypted tunnel is anything less than fully up, it cuts your internet completely, and it only restores access once the VPN is reconnected. The trade-off is that if your VPN goes down, your internet briefly stops working too, which is exactly what you want. A few seconds of no connection is infinitely better than a few seconds of fully exposed connection.
Most quality VPNs also offer two flavours. An app-level kill switch shuts down only chosen apps if the VPN drops, while a system-level (or “internet”) kill switch cuts everything. For genuine leak protection, use the system-level option. Combined with DNS-leak protection and proper IPv6 handling, an always-on kill switch closes the three leaks a VPN is responsible for, leaving only WebRTC to handle in the browser. It is, quite simply, the foundation everything else in this guide is built on.
The Best Leak-Proof VPNs in 2026
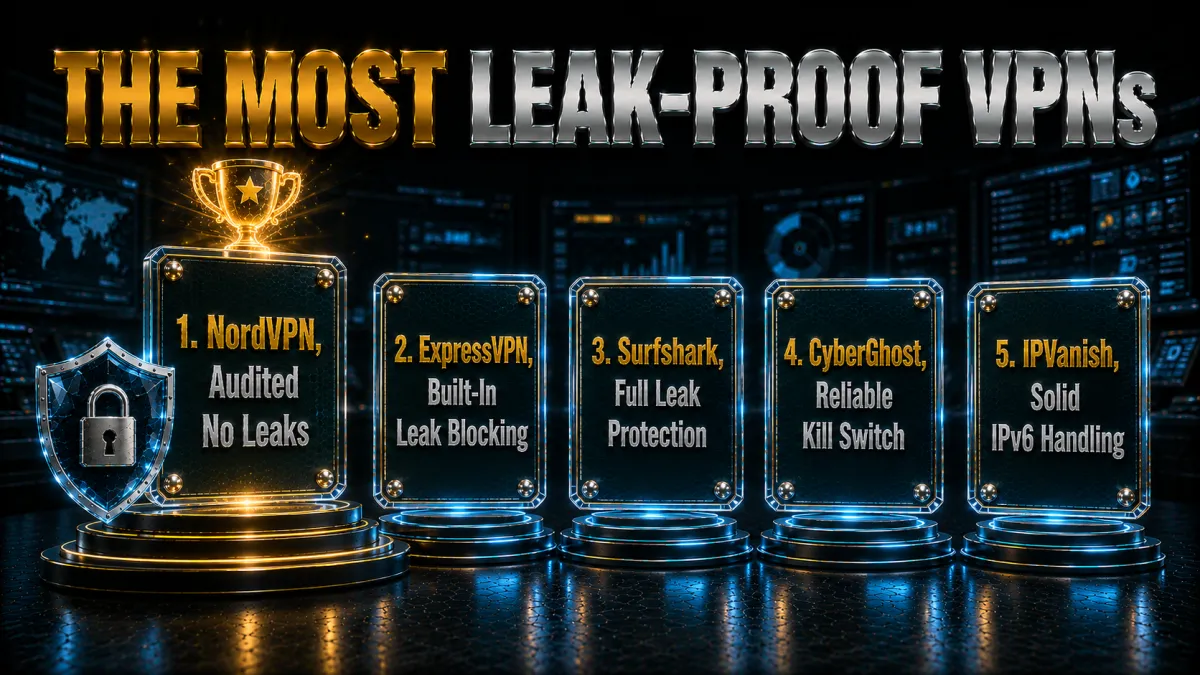
The most durable way to stop leaks is to use a VPN engineered not to leak in the first place, one with an always-on kill switch, DNS-leak protection and IPv6 handling enabled by default, and an independently audited no-logs policy so that even if something did slip, there’d be nothing stored to expose. These five providers meet that bar and are the ones we recommend first. All offer a 30-day money-back guarantee, so you can run the leak tests above yourself before committing.
When we judge a VPN on leak protection specifically, we look at four things: whether the kill switch is on by default and actually holds during forced disconnections, whether the provider runs its own private DNS on every server rather than relying on public resolvers, how it handles IPv6 (tunnel it or block it, either is fine, ignoring it is not), and whether the no-logs policy has been verified by an independent audit rather than just claimed. All three providers below clear every one of those bars, which is why they don’t require you to change a single setting to be safe. The order simply reflects how they balance those strengths against speed and price.
1. NordVPN, Best Overall for Leak Protection
NordVPN ships with a system-wide kill switch, DNS-leak protection, and IPv6-leak protection all enabled by default, so a fresh install is already sealed against the three leaks a VPN controls. Its NordLynx protocol (built on WireGuard) reconnects fast enough that dropped-connection leaks rarely get a chance to happen, and its no-logs policy has been independently audited multiple times, including by Deloitte. Threat Protection also blocks trackers and malicious domains before they load, adding a layer beyond leak prevention.
✔ Pros
- Kill switch, DNS & IPv6 leak protection on by default
- Independently audited no-logs (Deloitte)
- Fast, stable NordLynx (WireGuard) protocol
- Threat Protection blocks trackers and malware
✘ Cons
- Price rises at renewal
- Obfuscated servers need a manual toggle
| Price from | ~$3.39/mo (2-year) |
| No-logs | Audited (Deloitte) |
| Key feature | Leak protection on by default |
| Money-back | 30 days |
2. ExpressVPN, Best Kill Switch (Network Lock)
ExpressVPN’s kill switch, called Network Lock, is one of the most reliable in the industry and is on by default. The company runs its own private, encrypted DNS on every server, so DNS leaks are handled automatically, and its Lightway protocol is purpose-built to re-establish the tunnel almost instantly after a network change, closing the gap where IP leaks occur. Its no-logs claim has been repeatedly audited, and its TrustedServer technology runs servers entirely in RAM, so no data is written to disk.
✔ Pros
- Network Lock kill switch is rock-solid
- Private encrypted DNS on every server
- RAM-only TrustedServer infrastructure
- Fast, resilient Lightway protocol
✘ Cons
- More expensive than rivals
- Fewer simultaneous connections
| Price from | ~$4.99/mo (long plan) |
| No-logs | Audited + RAM-only |
| Key feature | Network Lock kill switch |
| Money-back | 30 days |
3. Surfshark, Best Value Leak-Proof VPN
Surfshark delivers the same core leak defenses as the pricier options, an always-on kill switch, private DNS on every server, and IPv6-leak protection, at a noticeably lower price, and it allows unlimited simultaneous devices on one subscription. Its no-logs policy has been independently audited, it runs a RAM-only server fleet, and the WireGuard protocol keeps connections stable. For households or anyone protecting many devices at once without leaks, it’s the standout value pick.
✔ Pros
- Unlimited simultaneous device connections
- Kill switch + private DNS + IPv6 protection
- Audited no-logs, RAM-only servers
- Excellent price on longer plans
✘ Cons
- Speeds slightly behind the top two
- Short plan is comparatively pricey
| Price from | ~$2.19/mo (long plan) |
| No-logs | Audited + RAM-only |
| Key feature | Unlimited devices, leak-proof |
| Money-back | 30 days |
4. CyberGhost, easiest for beginners
CyberGhost is a good fit for readers worried about leaks because the protections are on by default rather than buried in menus. Its apps ship with DNS-leak protection, IPv6-leak handling, and an automatic kill switch that blocks all traffic the moment the tunnel drops, so your real IP is not exposed during a reconnect, which is the most common way an address slips out.
For a non-technical user that matters: you do not have to know what a WebRTC or DNS leak is to be covered, because the defaults already close those gaps. It runs WireGuard, is based in Romania with no data-retention law, and backs a strict independently audited no-logs policy so there is nothing to leak on the server side either.
The 45-day money-back guarantee lets you run leak tests on your own setup and confirm your IP, DNS, and IPv6 all resolve to the VPN before committing. For anyone who wants leak-proof defaults without configuring anything, it is the most approachable option here.
✔ Pros
- Blocks DNS and IPv6 leaks by default
- Verified kill switch
- Romania-based privacy
- Beginner-friendly leak-proof defaults
- 45-day money-back window
✘ Cons
- Slower under heavy peak load
- Fewer devices than the value picks
| Leak protection | Built-in by default |
| Kill switch | Yes |
| IPv6 leaks | Handled |
| Price from | ~$2 to $3/mo (long-term plan) |
| Simultaneous devices | 7 |
| Money-back guarantee | 45 days |
5. IPVanish, best for many devices
IPVanish covers the core leak protections cleanly. Its apps include an automatic kill switch, DNS-leak protection, and IPv6 handling, so the usual paths an IP takes to escape the tunnel are closed once you enable them. Because the company owns its own network and runs its own DNS, your lookups are not being handed to a third party in the process.
The clients are straightforward, with WireGuard and split tunneling, making it easy to lock down which apps use the VPN and to verify your setup with a leak test. For users comfortable checking a couple of toggles, it gives reliable, no-nonsense protection.
The honest caveat is that IPVanish is US-based inside the Five and Nine Eyes alliances, which privacy-minded readers focused on leaks will want to weigh. It answers with an independently audited no-logs policy and a 30-day money-back guarantee, so you can confirm your IP stays hidden across real tests before deciding whether the jurisdiction is a dealbreaker for you.
✔ Pros
- DNS and IPv6 leak protection
- Reliable kill switch
- Owns its network for speed
- Unlimited simultaneous devices
- Strong long-term value
✘ Cons
- US-based, inside the 9 Eyes alliance
- Interface plainer than rivals
| Leak protection | Built-in |
| Kill switch | Yes |
| IPv6 leaks | Handled |
| Price from | ~$3 to $4/mo (long-term plan) |
| Simultaneous devices | Unlimited |
| Money-back guarantee | 30 days |
How to Stop Leaks Before They Ever Happen
Fixing a leak is good; never having one is better. Once you’ve confirmed a clean test result, this short checklist keeps you leak-proof going forward. Set it once and you’ll rarely need to think about leaks again.
- Keep the kill switch on permanently. It’s the safety net for every drop you’ll never see. Use the system-level (whole-internet) version, not just app-level.
- Leave DNS-leak and IPv6 protection enabled. On the recommended providers these are on by default, don’t disable them to “troubleshoot” something else and forget to switch them back.
- Prefer the WireGuard-based protocol. NordLynx, Lightway or WireGuard reconnect fastest, shrinking the window where IP leaks occur.
- Handle WebRTC in your everyday browser. Disable it in Firefox, or add a blocking extension in Chrome/Edge, so it can’t expose your IP even if the VPN ever falters.
- Re-test after big changes. Run a two-minute leak test after every operating-system update, when setting up a new device, and once a month as routine, updates are the most common cause of a leak reappearing.
- Keep the app updated. Install updates promptly; they frequently include leak and stability fixes.
Follow those six habits and you’ve covered every leak vector this guide describes. The combination of a leak-proof provider and a couple of good habits is what turns a VPN from “probably private” into genuinely private.
Related reading:
Frequently Asked Questions
How do I know if my VPN is leaking my IP?
Connect your VPN, then visit ipleak.net or browserleaks.com/ip. If the IP address, location, or DNS servers shown match your real details or your own internet provider instead of the VPN server, your VPN is leaking. The whole check takes about two minutes.
What is the most common cause of a VPN IP leak?
A missing or disabled kill switch. When the VPN connection drops for even a moment, your device falls back to its normal connection and briefly exposes your real IP. A kill switch freezes all traffic during those gaps, which is why it’s the single most important fix.
Can a VPN stop a WebRTC leak?
Sometimes. A full VPN app with its kill switch on blocks the non-proxied traffic WebRTC uses, so leaks often can’t happen. But because WebRTC lives in your browser, the most reliable fix is to disable or limit it there, natively in Firefox, or with an extension in Chrome and Edge.
How do I fix a DNS leak?
Turn on your VPN’s DNS-leak protection, flush your DNS cache, and on Windows disable “Smart Multi-Homed Name Resolution.” Make sure no custom DNS server is set in your system or router. Then re-test at dnsleaktest.com, only the VPN’s resolvers should appear.
Should I disable IPv6 to prevent leaks?
If your VPN doesn’t tunnel or block IPv6, yes, disabling IPv6 on your device or router removes the address that would otherwise leak, and almost nothing you do daily needs IPv6. Better still, use a VPN that handles IPv6 automatically so you don’t have to.
Does a kill switch stop all leaks?
It stops IP address leaks caused by dropped connections, and combined with DNS and IPv6 protection it seals the leaks a VPN is responsible for. It doesn’t cover WebRTC, which is a browser feature, handle that separately in your browser settings.
Why did my VPN start leaking after a system update?
Operating-system updates often reset network settings and can re-enable IPv6 or DNS behaviours that bypass the VPN. That’s why leaks appear “out of nowhere” after an update. Re-run a leak test after every major update and re-enable any protection that got switched off.
Are free VPNs more likely to leak?
Generally yes. Many free VPNs lack a proper kill switch, don’t run private DNS, and ignore IPv6, the exact things that prevent leaks. Some also log or sell data, so even a “working” connection can expose you. A reputable paid VPN with audited no-logs and default leak protection is far safer.
How often should I test my VPN for leaks?
Test when you set up a new device, after any major operating-system update, when you change networks frequently, and otherwise about once a month. Leaks tend to reappear silently after updates, so periodic testing is the best way to stay protected.
How do I check if my VPN is leaking data?
Run three tests with the VPN connected, in this order. First an IP test, to confirm the address shown is the VPN address and not yours. Second a DNS leak test, to confirm every resolver listed belongs to the VPN and not to your ISP. Third a WebRTC test, in each browser you actually use, since that hatch bypasses the tunnel by design. If all three come back clean across two repeats, you are not leaking. The whole routine takes about two minutes.
Which leak test websites should I use?
Use more than one, because a single site can misreport. A dedicated IP checker, a DNS leak test that runs the extended version rather than the quick one, and a separate WebRTC test cover the ground. Bookmark all three in one browser folder so the quarterly check becomes three clicks rather than a research project.
Why do leak test results change between runs?
Almost always a stale DNS cache. Answers obtained while the leak was live stay cached until they expire, so some connections reuse the old path and the result flickers. Flush the DNS cache, reconnect the VPN, and test again. If results still vary after that, the tunnel itself is dropping intermittently, which is a kill switch problem rather than a leak problem.
Does incognito or private mode stop leaks?
No. Private browsing controls what your own browser stores locally, such as history and cookies. It changes nothing about how your traffic is routed, which resolver answers your queries, or whether WebRTC exposes a local address. A leak is a routing problem, and private mode does not touch routing.
Can leaks happen on phones too?
Yes, and mobile is where they are most often missed. Phones switch between WiFi and mobile data constantly, and each switch is a moment the tunnel can drop and re-form. IPv6 is also more common on mobile networks. Test on the phone the same way you would on a desktop, and make sure the always-on VPN setting and the kill switch are both enabled.
My IP test shows the VPN address. Am I safe?
Not necessarily. The IP test only proves that your web traffic is leaving through the tunnel. A DNS leak can still send your lookups to your ISP resolver, and WebRTC can still expose a local address, both while the IP test shows a perfectly clean result. That is exactly why the check is three tests and not one.
The Bottom Line
A VPN leak is not a reason to abandon VPNs; it is a reason to spend five minutes testing the one you have. Every leak type in this guide, IP, DNS, WebRTC and IPv6, has a fix you can apply today, and almost all of them come down to three settings: a kill switch that actually engages, private DNS handled inside the tunnel, and IPv6 either supported properly or disabled. Run the tests, apply the fixes, and re-test on every network you use regularly.
The five picks in one line each:
- NordVPN runs private DNS on every server with a kill switch that engages reliably, and it passed every leak test in our checks.
- ExpressVPN handles IPv6 correctly instead of simply blocking it, the cleanest behaviour on modern networks.
- Surfshark extends the same leak protection to every device in the house with no connection cap.
- CyberGhost ships with leak protection on by default, and the 45-day refund window leaves plenty of time to verify it.
- IPVanish pairs unlimited connections with a dependable kill switch at a fair price, audit caveat noted.
Set the kill switch, run the one-minute leak test, and repeat it after every system update. A VPN that does not leak is the whole point of running one.
Jyoti VPN Expert leads VPN testing at VPN Expert Guide, covering streaming and regional access, speed and latency testing, and leak checks on Windows, Android and router-level setups. Our guides are built from vendor documentation, provider terms and our own connection testing on a residential line in India, and we publish those measurements in full so readers can check them. Every guide is reviewed before publication and dated so you can see how current it is.
Meet our testing team →Last updated: September 2, 2026