
What Is DNS and Why It Matters: The Internet’s Phonebook, Explained Properly
Every single thing you do online begins with a step you never see: a DNS lookup, the internet’s phonebook translating website names into the numeric addresses computers use. It runs billions of times a day and quietly shapes your speed, security, and privacy more than almost any setting you have touched. This guide explains DNS from the ground up, why it matters to ordinary users and not just engineers, and how VPNs with private DNS fix the default setup’s privacy hole.
What DNS actually is
Strip the acronym and DNS is one simple, enormous idea.
- A translation service for names. Humans remember names like vpnexpertguide.com; networks route by numeric IP addresses. DNS is the global system that turns one into the other, billions of times a day, in fractions of a second.
- The phonebook analogy, with one upgrade. Like a phonebook, DNS maps names to numbers; unlike a phonebook, it updates constantly, sites change addresses, load-balance across many, and DNS keeps every copy of the book current.
- Invisible by design. When DNS works, you never think about it; the page simply loads. You only meet DNS by name when it breaks, leaks, or slows down, which is exactly why understanding it pays off.
- Older than the web itself. DNS predates websites: it was built in the 1980s to replace hand-maintained address lists, and the same core design still carries the modern internet. Durable, decentralised, and, in its original form, completely unencrypted, which becomes important later.
How a DNS lookup actually works
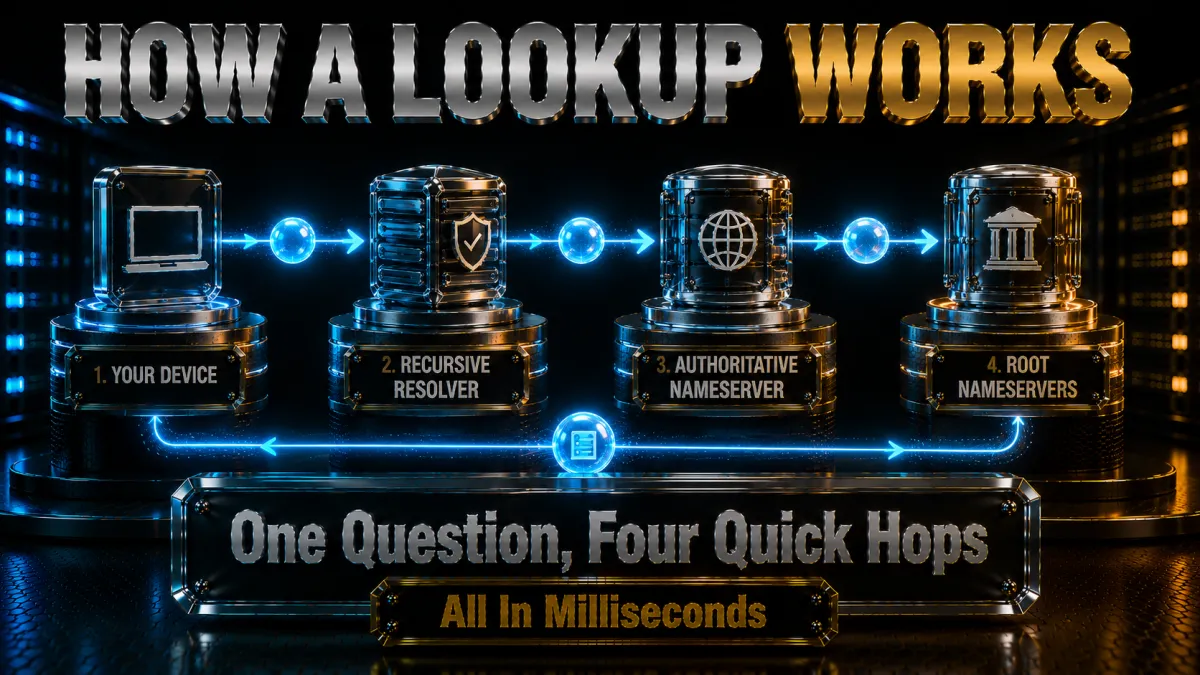
The whole journey takes milliseconds; here it is in slow motion.
- Step one: your device checks its cache. If you visited the site recently, the answer is already stored locally and the lookup ends before it starts. Caching is why second visits feel snappier.
- Step two: the question goes to a resolver. No cached answer means your device asks its configured DNS resolver, by default, one run by your internet provider or network operator. This resolver is the character that matters most in the privacy story.
- Step three: the resolver walks the hierarchy. If the resolver does not know either, it asks the root servers, which point to the servers for .com or your country’s domain ending, which point to the specific site’s own name servers, which hold the final answer.
- Step four: the answer comes back and gets cached. The IP address returns down the chain, every stop caches it for a set time, and your browser finally opens the actual connection to the site.
- All of this happens per name, constantly. A single modern webpage can trigger dozens of lookups for scripts, images, and ad domains. DNS is not an occasional event; it is a continuous hum underneath everything.
The types of DNS servers, and why the differences matter
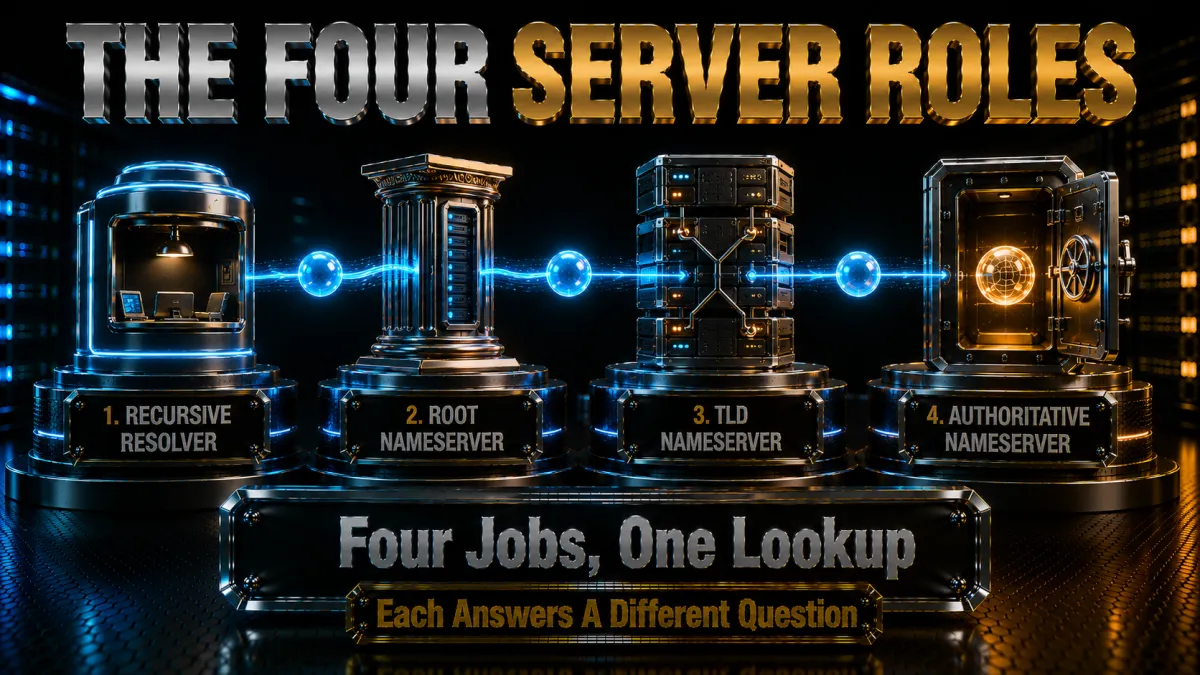
Four kinds of server share the work; knowing them makes every DNS conversation clearer.
- Recursive resolvers: the ones that serve you. These take your question and chase the full answer through the hierarchy. Your ISP runs one; public options like Cloudflare, Google, and Quad9 run famous alternatives; VPNs run private ones. Choosing your resolver is the one DNS choice ordinary users actually make.
- Root servers: the top of the tree. A small, globally distributed set of servers that know where every domain ending lives. You never talk to them directly; your resolver does.
- TLD servers: one per domain ending. The .com servers know where every .com’s name servers are, and so on for .org, .in, .co.uk, and the rest. Another layer you benefit from without touching.
- Authoritative servers: the final word. Each website’s own name servers hold its actual records: which IPs serve it, where its mail goes, and more. When a site changes hosting, these records change, and the world’s caches gradually catch up.
- Why the distinction pays off. Almost every practical DNS decision, privacy, speed, filtering, parental controls, happens at the resolver layer. The rest of the tree is shared infrastructure; the resolver is personal.
Why DNS matters for everyday users and businesses
Not just plumbing: DNS quietly decides real outcomes for both.
- It is on the critical path of everything. Slow DNS makes every site feel slow, because nothing loads until the name resolves. A sluggish resolver taxes your whole internet experience invisibly.
- It is a complete record of where you go. Whoever answers your lookups sees every domain your household visits, timestamped. For businesses, the same applies across the whole staff. That visibility is the privacy story in one sentence.
- It is a control point. Network operators use DNS to block and filter: schools filter categories, offices block services, some ISPs redirect typos to ad pages. Useful or annoying, it all happens at the resolver.
- It is a security layer when used well. Filtering resolvers block known-malicious domains before a connection ever opens, one of the cheapest protections available to families and businesses alike.
- For businesses, it is uptime itself. A company whose DNS records break vanishes from the internet with its servers running fine. This is why DNS management is a discipline, and why record changes get scheduled carefully.
DNS and your security: where the risks actually live
The original DNS design assumed a politer internet; these are the consequences.
- Classic DNS is unencrypted. Traditional lookups travel as plain text, so anyone on the network path, cafe Wi-Fi included, can read exactly which sites you are resolving, even while the sites themselves use HTTPS.
- Spoofing and cache poisoning are real attack classes. If an attacker answers your lookup faster than the honest resolver, or poisons a cache, your device connects to their server believing the name. Modern mitigations help; the risk shaped the whole encrypted-DNS movement.
- Malicious networks weaponise the resolver. A rogue hotspot controls the DNS it hands you, and can answer any name with any address it likes. This is precisely why DNS handling matters so much in VPN evaluations.
- Encrypted DNS closes the eavesdropping half. DNS over HTTPS and DNS over TLS wrap lookups in encryption, hiding them from the local network. Browsers and operating systems increasingly support it; it protects the question in transit, though the resolver you choose still sees it.
- Filtering resolvers add a shield. Resolvers that refuse to answer for known-malicious domains stop phishing and malware connections at the cheapest possible point: before they exist.
DNS leaks: where VPNs enter the story
This is the junction where DNS knowledge becomes VPN advice.
- The leak, defined. You connect a VPN expecting privacy, but your device keeps sending DNS lookups outside the tunnel to the ISP’s resolver. Your traffic detours; your destination list still reads like an open diary. That is a DNS leak.
- Why leaks happen. Operating systems cling to configured resolvers, some setups race multiple lookups for speed, and badly built VPN apps simply fail to capture DNS traffic. It is the most common way cheap VPNs fail quietly.
- The proper fix is architectural. A well-built VPN runs its own DNS resolvers, answers every lookup inside the encrypted tunnel, and firewalls any lookup that tries to escape. Your ISP then sees neither traffic nor questions.
- Testing takes thirty seconds. Every reputable provider offers a leak test page: connect, run it, and confirm the resolver shown belongs to the VPN, not your ISP. Do it once at setup and after major OS updates.
- This is a headline criterion, not a footnote. All five picks below run private DNS on their own infrastructure with leak protection built in. A VPN without that is a curtain with a gap down the middle.
How to choose your DNS setup in one minute
Three situations cover nearly every reader.
- You just want faster, safer defaults at home. Switch your router or device to a reputable public resolver, Cloudflare, Google, or the filtering-focused Quad9, and enable encrypted DNS where your OS offers it. Cost: nothing. Time: five minutes.
- You want your browsing history out of everyone’s logs. Public resolvers still see your lookups, and your ISP still sees your traffic. This is the job for a VPN with private DNS: one encrypted pipe, lookups answered inside it, nothing readable outside.
- You run a family network or small business. A filtering resolver, standalone or via a VPN’s blocking features, stops whole categories of trouble before connections open. Pair it with the leak test habit and the setup maintains itself.
- The honest hierarchy. Better resolver: good. Encrypted DNS: better. VPN with private DNS: the complete answer, because it protects the lookups and the traffic together.
The 5 best VPNs for private DNS in 2026
Ranked for this page’s criterion first: own-infrastructure DNS with proven leak protection, then speed, audits, and value.
1. NordVPN – Best overall private-DNS package
NordVPN answers every DNS concern this page raised: lookups resolve on Nord’s own DNS servers inside the encrypted tunnel, leak protection firewalls any stray query, and the whole arrangement sits under a no-logs policy verified by multiple independent audits on RAM-only infrastructure.
Threat Protection extends the DNS story usefully, blocking known-malicious domains at exactly the resolver layer this guide described, and NordLynx keeps the added privacy free of speed cost. The built-in leak test habit takes thirty seconds; the settings depth takes ten minutes once.
✔ Pros
- Own DNS on every connection, leak-protected
- Multiple independent no-logs audits
- Threat Protection blocks malicious domains
- NordLynx keeps speeds near-native
- RAM-only servers, Panama base
✘ Cons
- Denser settings than minimalist rivals
- Best price needs a longer plan
| Own DNS servers | Yes, all servers |
| DNS leak protection | Yes, built in |
| Domain filtering | Threat Protection |
| Audited no-logs | Yes, multiple audits |
| Devices | 10 |
| Money-back | 30 days |
2. ExpressVPN – Own DNS on every server, zero configuration
ExpressVPN’s signature architectural choice fits this page perfectly: every VPN server runs its own DNS resolver locally, so lookups never leave the box that carries your traffic, encrypted end to end with nothing outsourced. It is the cleanest DNS design in the industry, and it requires no configuration at all.
The RAM-only fleet, audited no-logs policy, and British Virgin Islands jurisdiction complete the trust file, and Lightway keeps everything instant. The price is the highest of the five and devices cap at eight; what you buy is architecture-grade privacy in a one-button app.
✔ Pros
- Private DNS runs on every server itself
- RAM-only fleet, audited no-logs
- Simplest apps of the five
- Excellent hostile-network reliability
- BVI jurisdiction
✘ Cons
- Most expensive of the five
- 8-device cap is the tightest here
| Own DNS servers | Yes, on each server |
| DNS leak protection | Yes, built in |
| Domain filtering | Limited |
| Audited no-logs | Yes, audited |
| Devices | 8 |
| Money-back | 30 days |
3. Surfshark – Private DNS plus filtering at the best price
Surfshark carries private DNS on every server, leak protection, and CleanWeb, its resolver-level blocker for ads and malicious domains, into the lowest long-term price of the five with unlimited devices. For a household wanting the DNS-privacy upgrade on every gadget at once, the arithmetic is unbeatable.
The no-logs policy is independently audited. Placed honestly: peak speeds trail the top two a step and the Netherlands base sits inside the EU. At this per-device price, the trade stays comfortable.
✔ Pros
- Private DNS with leak protection
- CleanWeb filters at the DNS layer
- Lowest long-term price of the five
- Unlimited simultaneous devices
- Audited no-logs policy
✘ Cons
- Peak speeds behind the top two
- Netherlands base, inside the EU
| Own DNS servers | Yes |
| DNS leak protection | Yes |
| Domain filtering | CleanWeb |
| Audited no-logs | Yes, audited |
| Devices | Unlimited |
| Money-back | 30 days |
4. CyberGhost – Easiest private-DNS start
CyberGhost handles DNS the way beginners need it handled: privately, automatically, and without a settings screen in sight. Lookups resolve on CyberGhost infrastructure inside the tunnel, leak protection is standard, and the audited no-logs policy comes with regular transparency reports.
The 45-day money-back guarantee remains the longest evaluation window of the five, plenty of time to run leak tests on every network you actually use. Power users will want more dials; everyone else will not miss them.
✔ Pros
- Private DNS handled automatically
- 45-day refund, longest here
- Audited no-logs with transparency reports
- Plainest-language apps of the five
- Huge server network
✘ Cons
- Lighter advanced controls
- Speeds good rather than leading
| Own DNS servers | Yes |
| DNS leak protection | Yes |
| Domain filtering | Basic blocker |
| Audited no-logs | Yes, audited |
| Devices | 7 |
| Money-back | 45 days |
5. IPVanish – Fast, unlimited, DNS covered
IPVanish runs its own DNS with leak protection, pairs it with brisk sustained speeds, and allows unlimited simultaneous connections at a fair price. As the straightforward workhorse of the five, it covers this page’s core requirement without ceremony.
The honest fifth-place note stands: US jurisdiction inside the major intelligence alliance and a lighter independent audit history than the leaders. For ordinary threat models the package is fair value; for privacy-first buyers, the top of the list is the address.
✔ Pros
- Own DNS with leak protection
- Consistently brisk speeds
- Unlimited simultaneous connections
- Fair pricing
- Simple apps everywhere
✘ Cons
- US jurisdiction
- Lighter audit history than the leaders
| Own DNS servers | Yes |
| DNS leak protection | Yes |
| Domain filtering | No |
| Audited no-logs | Policy in place, lighter audit history |
| Devices | Unlimited |
| Money-back | 30 days |
| Feature | NordVPN | ExpressVPN | Surfshark | CyberGhost | IPVanish |
|---|---|---|---|---|---|
| Own DNS servers | All servers | On each server | Yes | Yes | Yes |
| Leak protection | Built in | Built in | Yes | Yes | Yes |
| DNS-level filtering | Threat Protection | Limited | CleanWeb | Basic | No |
| Audited no-logs | Multiple audits | Audited | Audited | Audited | Lighter history |
| Devices | 10 | 8 | Unlimited | 7 | Unlimited |
| Money-back | 30 days | 30 days | 30 days | 45 days | 30 days |
How to change your DNS settings, device by device
For the no-VPN improvements, here is where the setting lives everywhere.
- On the router: the whole-home change. Set your preferred resolver in the router’s WAN or DHCP settings and every device on the network inherits it automatically. One change, full coverage, and the reason router-level is the recommended starting point.
- Windows and macOS: per-device control. Network settings on either OS accept custom DNS servers per connection, useful for laptops that roam between networks with different needs.
- Phones: per-network or private DNS. iOS sets DNS per Wi-Fi network; Android’s Private DNS setting applies an encrypted resolver across every network at once, one of the tidiest DNS features on any platform.
- Encrypted DNS toggles live in browsers and OS settings. DNS over HTTPS options appear in browser privacy settings and modern OS network panels; enable them to protect lookups in transit even before any VPN enters the picture.
- With a VPN connected, leave DNS alone. The VPN’s own resolvers take over inside the tunnel by design; manually overriding them can reopen the very leak the app closed. Set and forget applies.
VPN vs Smart DNS: cousins, not twins
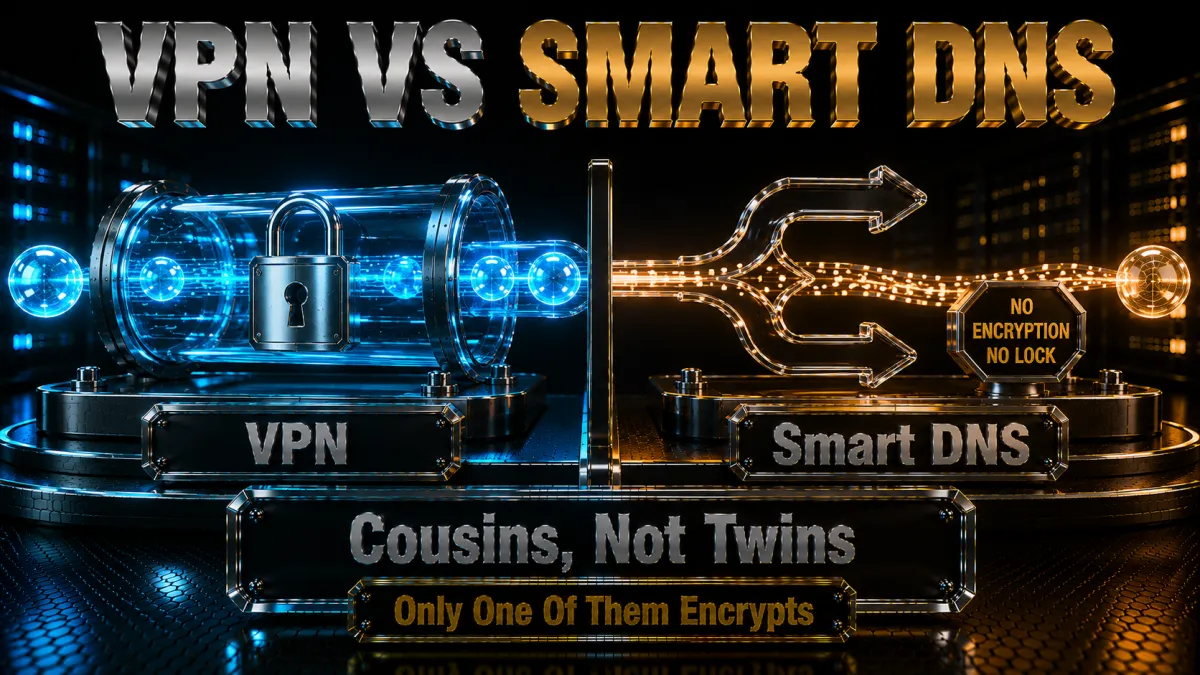
Providers often bundle both, and the names invite confusion worth clearing.
- Smart DNS reroutes lookups, not traffic. It answers DNS in ways that steer specific services through remote gateways, mainly so streaming devices show another region’s catalogue. Your actual traffic flows outside any tunnel.
- No encryption means no privacy. Smart DNS hides nothing from networks or ISPs and does not change your IP for most purposes. It is a convenience tool for devices that cannot run VPN apps, TVs and consoles chiefly.
- A VPN does everything Smart DNS does, plus the actual protection. Encrypted tunnel, swapped IP, private lookups. On any device that can run the app, the VPN is simply the superset.
- Use them where they fit. VPN on phones, laptops, and routers; Smart DNS on the smart TV that cannot install apps, with clear eyes about what it does and does not protect. Streaming platform terms apply to both.
Fixing DNS problems: leaks, stale caches, and slow lookups
The practical repair kit, in the order problems actually occur.
- Confirmed a leak? Fix the source. Enable the VPN’s leak protection toggle if it somehow sat off, update the app, and disable browser features that race lookups outside the tunnel. Re-test; the resolver shown should belong to the VPN.
- Flush the DNS cache after any fix. Devices cache old answers, including leaked or poisoned ones. A cache flush, one command on desktop, a reboot on phones, makes your device forget stale records and ask fresh questions through the now-clean path.
- Sites resolving to the wrong place? Same medicine. After a site changes hosting, or after you change resolvers, stale cache entries cause weird half-broken loading. Flush, retry, resolved in most cases.
- Everything slow to start loading? Time the resolver. If pages hesitate before loading begins, the resolver may be the drag: switch to a fast public option or your VPN’s own, and feel the difference immediately on lookup-heavy pages.
- Nothing resolving at all? Walk the chain. Check the device’s DNS setting, try a known-good resolver, reboot the router. DNS-dead-but-network-alive almost always sits in one of those three places.
Common DNS mistakes people make
Five recurring errors, each cheap to avoid.
- Assuming HTTPS hides which sites you visit. Page contents are encrypted; the DNS lookups announcing every domain are not, by default. This single misunderstanding sustains most DNS complacency.
- Believing a VPN automatically means private DNS. Cheap and free VPNs leak lookups constantly. The thirty-second leak test, not the marketing page, is the verification.
- Overriding VPN DNS with manual settings. Custom resolvers configured on top of a connected VPN can bypass the tunnel and reopen the diary. Inside the tunnel, the VPN’s resolvers are the private path.
- Never testing after OS updates. Updates reset network behaviour more often than anyone expects. A leak test after major updates keeps yesterday’s verification true today.
- Chasing exotic resolver lists. Obscure resolvers with grand claims are the DNS version of shady free VPNs. Reputable public options and audited VPN resolvers cover every real need.
Does DNS affect internet speed? The honest answer
Yes and no, in specific ways worth separating.
- DNS affects responsiveness, not bandwidth. Lookups happen before pages load, so a slow resolver adds hesitation to every first visit, while your download speed stays untouched. Snappiness and throughput are different feelings.
- Caching hides most of it. Repeat visits answer from cache, which is why a slow resolver feels like occasional stutter rather than constant drag, and why lookup-heavy pages expose it most.
- Geography matters for resolvers too. A resolver far away adds distance to every uncached question. Good public resolvers and VPN-run DNS both answer from nearby infrastructure, keeping the added time trivial.
- A VPN’s DNS is not a slowdown. Lookups inside the tunnel travel to resolvers hosted on or near the VPN’s own servers; the cost rounds to nothing against the privacy gained. Speed complaints about VPNs trace to server crowding, almost never to DNS.
Related reading:
Frequently Asked Questions
What is DNS in simple terms?
DNS, the Domain Name System, is the internet’s phonebook: it translates the website names humans type into the numeric IP addresses computers use to connect. Every site visit, app launch, and link click begins with a DNS lookup, usually completed in milliseconds by a resolver run by your internet provider or one you choose.
Why does DNS matter for ordinary users?
Three reasons: speed, because every page waits on lookups before loading; security, because filtering resolvers can block malicious sites before connections open; and privacy, because whoever answers your lookups sees a complete, timestamped list of every domain your household visits. The resolver choice quietly shapes all three.
Who sees my DNS queries?
By default, your internet provider or network operator, whose resolver answers them, plus anyone on the local network path when lookups travel unencrypted. Switching resolvers moves that visibility rather than removing it; encrypted DNS hides lookups in transit; a VPN with private DNS moves the whole question inside an encrypted tunnel.
What is a DNS leak?
A DNS leak is when your device sends lookups outside a connected VPN’s tunnel, typically to your ISP’s resolver, so your destination list stays visible even while your traffic is encrypted. It is the most common quiet failure of cheap VPNs, and a thirty-second leak test after setup confirms whether your tunnel handles lookups properly.
How do I know if my VPN is leaking DNS?
Connect the VPN, open your provider’s leak test page or any reputable DNS leak tester, and check which resolvers appear: they should belong to the VPN, not your internet provider. Test once at setup, after major OS updates, and any time network behaviour seems odd; it is the cheapest verification in privacy.
Should I use Google DNS, Cloudflare, or my ISP’s default?
Reputable public resolvers like Cloudflare and Google are typically faster and better-run than default ISP resolvers, and Quad9 adds malicious-domain filtering; all are free five-minute changes. Remember the trade: you move visibility from the ISP to the resolver operator. For removing that visibility from the path entirely, the VPN-with-private-DNS route is the complete answer.
What is DNS over HTTPS and should I enable it?
DNS over HTTPS wraps lookups in encryption so networks between you and the resolver cannot read or tamper with them; browsers and modern operating systems increasingly support it. Yes, enable it where offered; note that your chosen resolver still sees the queries, which is the remaining gap a VPN’s in-tunnel DNS closes.
Does changing DNS make my internet faster?
It can make browsing feel snappier if your current resolver is slow, because lookups precede every first visit; it never changes your actual bandwidth. The effect is most noticeable on lookup-heavy pages and vanishes on cached repeat visits. A nearby, well-run resolver keeps the hidden hesitation near zero.
What is Smart DNS and how is it different from a VPN?
Smart DNS steers lookups for specific services through remote gateways, mainly so devices like TVs show another region’s streaming catalogue; it encrypts nothing and hides nothing. A VPN encrypts all traffic, swaps your IP, and resolves lookups privately. Use Smart DNS for app-less devices; use the VPN everywhere it can run.
Can DNS be hacked or spoofed?
Attack classes exist: spoofed answers and cache poisoning can steer devices to impostor servers, and rogue networks control the DNS they hand out. Mitigations include modern resolver protections, encrypted DNS in transit, and, on untrusted networks, a VPN whose in-tunnel resolvers ignore whatever the hostile network offers.
How do I flush my DNS cache and when should I?
Flush after fixing leaks, changing resolvers, or when sites resolve strangely: on Windows via ipconfig /flushdns, on macOS via a terminal command, and on phones effectively via reboot or toggling airplane mode. Flushing makes the device forget stale or bad answers and ask fresh questions through the current, clean path.
Do all VPNs run their own DNS servers?
No, and it is a meaningful quality line: well-built VPNs answer lookups on their own infrastructure inside the tunnel with leak protection, while cheaper services outsource DNS or leak it entirely. All five picks on this page run private DNS with leak protection, which is precisely why they are the five.
Is DNS filtering good for families and small businesses?
Yes, it is one of the cheapest broad protections available: a filtering resolver refuses to answer for known-malicious domains, stopping phishing and malware connections before they open, and family-focused options add content categories. Standalone filtering resolvers or VPN features like Threat Protection and CleanWeb both work at this layer.
The Bottom Line
DNS is the internet’s quietest critical system: the phonebook consulted before every page, the control point where speed, security, and privacy all pass through one choice, and the diary your default setup writes at your internet provider without asking. Understanding it turns three invisible outcomes into decisions you actually make: pick a fast, reputable resolver and browsing sharpens; pick a filtering one and whole categories of trouble never connect; put lookups inside an encrypted tunnel with private DNS and the diary simply stops being written.
The five picks in one line each:
- NordVPN is the complete package: private leak-protected DNS, filtering, and the strongest audits.
- ExpressVPN runs the cleanest DNS architecture in the industry, resolvers on every server.
- Surfshark delivers private DNS plus CleanWeb filtering for every device at the lowest price.
- CyberGhost handles DNS privacy invisibly with the longest refund window at 45 days.
- IPVanish covers the essentials fast and unlimited, audit caveat noted honestly.
Run the thirty-second leak test whichever route you take, and enjoy the rare upgrade that makes the internet faster, safer, and more private in the same five minutes.
Jyoti VPN Expert leads VPN testing at VPN Expert Guide, covering streaming and regional access, speed and latency testing, and leak checks on Windows, Android and router-level setups. Our guides are built from vendor documentation, provider terms and our own connection testing on a residential line in India, and we publish those measurements in full so readers can check them. Every guide is reviewed before publication and dated so you can see how current it is.
Meet our testing team →Last updated: September 2, 2026